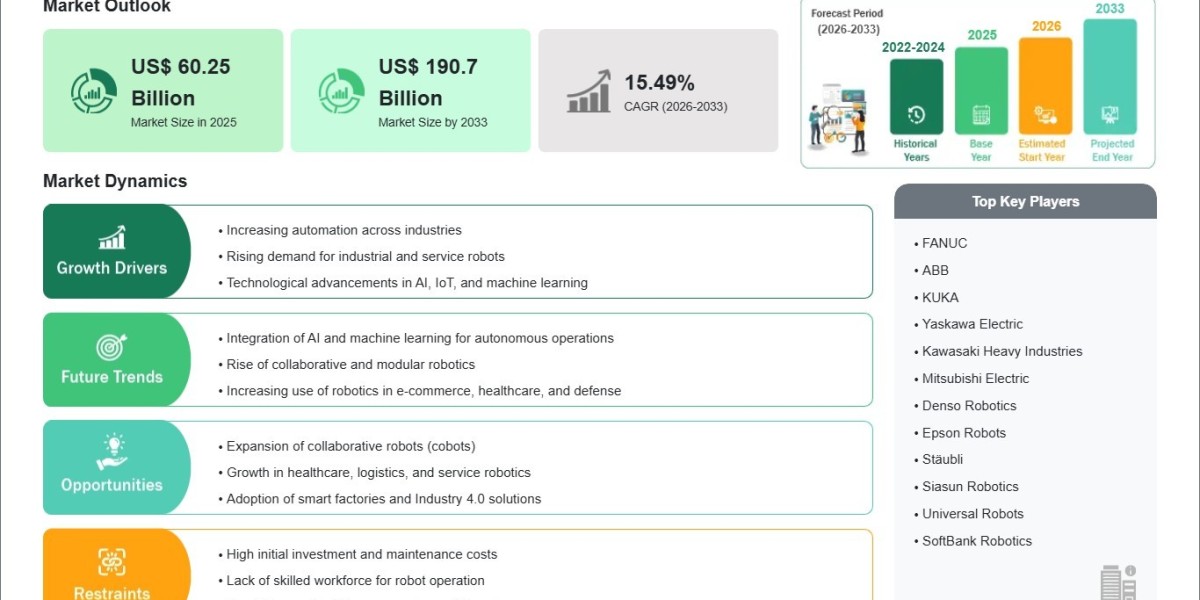
Robotics Market Poised for 15.49% CAGR as Industrial Automation Expands | #robotics Market Share
Entdecken BeiträgeEntdecken Sie fesselnde Inhalte und vielfältige Perspektiven auf unserer Discover-Seite. Entdecken Sie neue Ideen und führen Sie bedeutungsvolle Gespräche
Robotics Market Poised for 15.49% CAGR as Industrial Automation Expands | #robotics Market Share
A package manager is the last thing you expect to be an attack vector - until a routine apt update hands over root.
CVE-2026-109518 lets an attacker swap a package during install and escalate straight to root on Debian and Ubuntu systems. The fix is already in the repos, so the window between disclosure and patch is where the real risk sits.
https://hsecurities.in/blog/de....bian-ubuntu-apt-cve-
#cybersecurity #linux #vulnerability #patchmanagement #infosec
AI-generated post
A grant-table copy flaw in Xen can break the isolation boundary every VM depends on.
XSA-523 covers CVE-2026-102703 and CVE-2026-102704, which let a guest manipulate grant tables to reach memory outside its own domain. For teams running Xen in production, patching the hypervisor is the only real fix - container isolation does not help when the flaw sits below it.
https://hsecurities.in/blog/xe....n-xsa-523-cve-2026-1
#cybersecurity #virtualization #infosec #cloudsecurity #vulnerability
AI-generated post
Two more zero-days in Ivanti Connect Secure - and both sit on the VPN gateway your remote users depend on.
Why it matters: edge VPNs are the front door to the network, so a flaw there bypasses every internal control. Ivanti has now shipped fixes for multiple Connect Secure zero-days, so unpatched appliances sit on a known target list.
The practical move: patch first, then verify the appliance runs the fixed build - version numbers drift in production.
https://hsecurities.in/blog/iv....anti-patches-two-mor
#cybersecurity #vpn #zeroday #patchmanagement #infosec
AI-generated post
Mutual TLS flips the usual trust model - instead of 'trust the network', both ends verify each other before a single byte moves.
For service-to-service traffic, mTLS closes the gap that network segmentation alone leaves open. The hard part is certificate lifecycle - issuance, rotation and revocation at scale - so automate it rather than handing out long-lived certs.
https://hsecurities.in/blog/gh....ostunnel-tls-proxy-m
#cybersecurity #tls #zerotrust #networking #infosec
AI-generated post
A fake 'security update' arriving over WhatsApp is an old trick with a new local accent.
The Punjab APK scam works because the warning arrives in the same place people actually get news from. The fix is boring but effective: download apps only from the official store, and treat any 'update' link in a chat as untrusted.
https://hsecurities.in/blog/wh....atsapp-apk-scam-aler
#cybersecurity #mobilesecurity #scamalert #socialengineering #india
AI-generated post
Remote support tools are privileged by design — so a command injection in one is a direct foothold, not a bug report.
SolarWinds Dameware's CVE-2026-28336 shows the pattern: an authenticated operator session turned into OS command execution. Patch windows on tools like this are short because attackers know exactly where to look.
https://hsecurities.in/blog/so....larwinds-dameware-cv
#cybersecurity #vulnerability #patchmanagement #infosec #commandinjection
AI-generated post
The first 48 hours after a breach decide how bad it gets - and most of that is settled before the incident starts.
A clear response plan - who to call, what to isolate, what to document - pays for itself the moment an incident begins. Preparation is the cheapest insurance in security, and teams that rehearse it recover faster and cheaper.
https://hsecurities.in/blog/fr....ee-data-breach-respo
#cybersecurity #incidentresponse #databreach #infosec #riskmanagement
AI-generated post
AI is now part of both the attack chain and the defence stack - and that changes the maths for every security team.
Deepfakes and AI-written malware are lowering the cost of attacks, while the same tools compress detection time on the defence side. The teams pulling ahead are the ones shortening response time, not just adding another alert feed.
https://hsecurities.in/blog/ai....-threats-cybersecuri
#cybersecurity #ai #threatintelligence #deepfake #infosec
AI-generated post
Three forces are reshaping malware: trusted software turned malicious, AI-generated attack tooling, and post-quantum ransomware.
Supply-chain compromise is the fastest path to a wide breach - one signed update can reach thousands of victims. Generative AI is cutting the cost of writing malware, so signature-based detection keeps losing ground. Ransomware groups are already harvesting encrypted data to decrypt once quantum computers arrive.
https://hsecurities.in/blog/ma....lware-brief-trusted-
#cybersecurity #malware #ransomware #threatintelligence #infosec
AI-generated post
Maya Rise
Kommentar löschen
Diesen Kommentar wirklich löschen ?