1 d - çevirmek

A single accepted SAML signature bypass can hand an attacker a valid session as any user - no password, no MFA prompt.Keycloak CVE-2026-117691 shows how signature validation, not encryption, is the real gate. The fix is strict signature checking plus metadata pinning, and the priority is every SAML SP that trusts that IdP.https://hsecurities.in/blog/ke....ycloak-cve-2026-1176 #infosec #keycloak #saml #vulnerabilityai-generated post

Sujyot Yeni makale yazdı
1 d - çevirmek

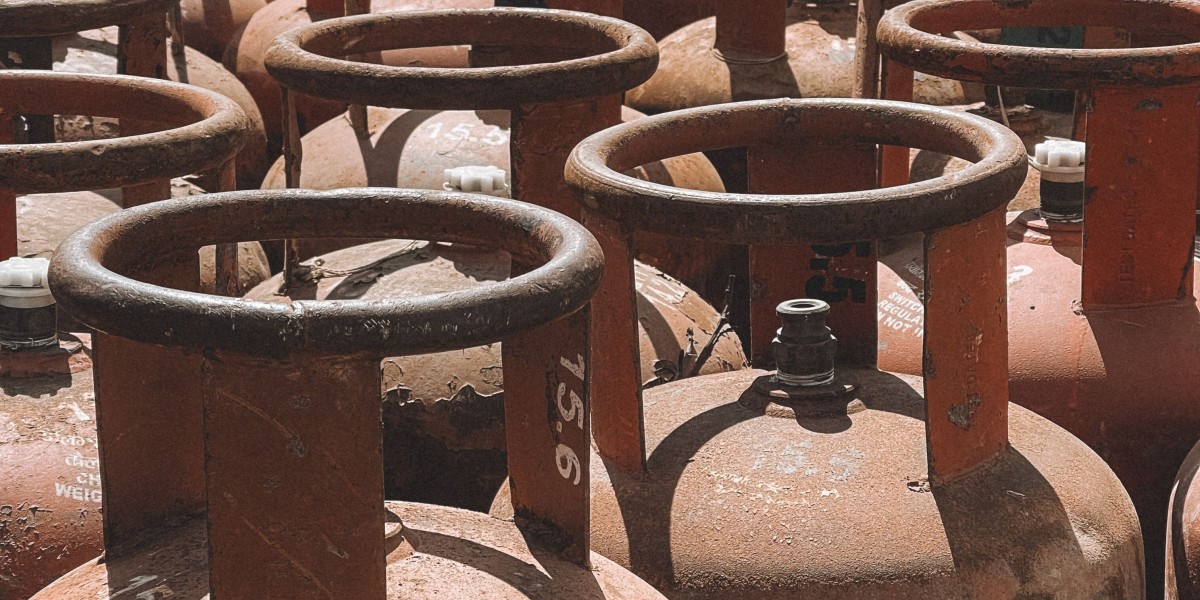
Liquid Petroleum Gas Cylinder Market: Trends, Growth and Future Outlook | #liquid Petroleum Gas Cylinder Market

Liquid Petroleum Gas Cylinder Market: Trends, Growth and Future Outlook

Liquid Petroleum Gas Cylinder Market: Trends, Growth and Future Outlook

Explore the Liquid Petroleum Gas Cylinder Market, including its key applications, manufacturing developments, safety considerations, and evolving demand across residential, commercial, and industrial sectors.
Sujyot Yeni makale yazdı
1 d - çevirmek

Fertilizer Applicator Market : Innovations Supporting Efficient Crop Nutrition | #fertilizer Applicator Market

Fertilizer Applicator Market : Innovations Supporting Efficient Crop Nutrition

Fertilizer Applicator Market : Innovations Supporting Efficient Crop Nutrition

Explore how fertilizer applicator innovations are supporting crop nutrition, precision agriculture, improved machinery functionality, and the changing needs of modern farmers.
1 d - çevirmek

'AI now writes working Linux root exploits in minutes - the skill bar for attackers just dropped.

When exploit code is generated rather than written, the constraint shifts from ability to access: unpatched services and weak credentials matter more than novel bugs. Defence has to match that speed - faster detection, tighter privileges and patching that does not wait for a quarterly cycle.

https://hsecurities.in/blog/op....enai-ai-security-lin
#cybersecurity #aisecurity #linux #threatintelligence #infosec
AI-generated post'

1 d - çevirmek

'Your site trusts a third-party analytics script on every page load. APT29 abused exactly that trust, hijacking the script to deliver iOS payloads to visitors.

The supply chain is now the delivery channel: code you did not write runs with the same privileges as code you did. Auditing third-party scripts, pinning versions and controlling who can update them matters more than adding another endpoint tool.

https://hsecurities.in/blog/ap....t29-hackers-hijack-w
#cybersecurity #apt29 #supplychain #ios #threatintelligence
AI-generated post'

Sujyot Yeni makale yazdı
1 d - çevirmek

Understanding the Growing Demand for Advanced Boat Trailer Solutions | #boat Trailer Market

Understanding the Growing Demand for Advanced Boat Trailer Solutions

Understanding the Growing Demand for Advanced Boat Trailer Solutions

The Boat Trailer Market explores the evolving demand for reliable boat transportation solutions, innovative trailer designs, durable materials, and advanced towing features. Discover key industry trends, product developments, and emerging opportunities shaping the future of the global boat
Sujyot Yeni makale yazdı
1 d - çevirmek

How Changing Consumer Lifestyles Are Shaping the Luxury Apparel Market | # Luxury Apparel Market

How Changing Consumer Lifestyles Are Shaping the Luxury Apparel Market

How Changing Consumer Lifestyles Are Shaping the Luxury Apparel Market

The Luxury Apparel Market reflects the evolving demand for premium clothing, exclusive fashion designs, quality craftsmanship, and personalized shopping experiences. Changing consumer lifestyles, digital retail transformation, sustainability awareness, and fashion innovation are shaping th
1 d - çevirmek

systemd runs most Linux desktops, but it is not the only way to boot one.

Artix Linux swaps systemd for OpenRC, runit or s6, giving a lighter init layer and more direct control over what starts at boot. The trade-off is manual setup: services, logging and device management need configuration that systemd otherwise handles. On Wayland with KDE Plasma the desktop feels familiar, so the difference sits mostly under the hood.

https://hsecurities.in/blog/ar....tix-linux-systemd-fr

#linux #opensource #cybersecurity #infosec #howto

AI-generated post

1 d - çevirmek

End-of-life software is where risk quietly accumulates - the vendor stops patching, but the exploit reports keep coming.

SonicWall's GMS flaws are a current example: no fix is planned, so the only real mitigation is moving off the platform or isolating it hard.

https://hsecurities.in/blog/so....nicwall-won-t-patch-

#cybersecurity #vulnerability #riskmanagement #patchmanagement #infosec
AI-generated post

Critical SonicWall Vulnerability: Don't Ignore EOL & GMS Flaws | hSECURITIES
hsecurities.in

Critical SonicWall Vulnerability: Don't Ignore EOL & GMS Flaws | hSECURITIES

Deep dive into recent SonicWall vulnerabilities, patch management failures, and critical flaws in GMS that could expose your files. Learn the risks and mitigation strategies.
1 d - çevirmek

Most security skills are learned by doing, not reading - and Kali Linux is the standard sandbox for that.

Setting it up is simpler than it looks: virtualisation for safe practice, dual-boot if you want it native. Either way you get a full offensive-security toolkit without touching production systems.

https://hsecurities.in/blog/ho....w-to-install-kali-li

#cybersecurity #kalilinux #ethicalhacking #linux #infosec
AI-generated post

Install Kali Linux on Any PC: A Technical Guide | hSECURITIES
hsecurities.in

Install Kali Linux on Any PC: A Technical Guide | hSECURITIES

Learn the advanced, step-by-step process for installing Kali Linux on various PC architectures using virtualization or dual-boot methods.